KOLVerse
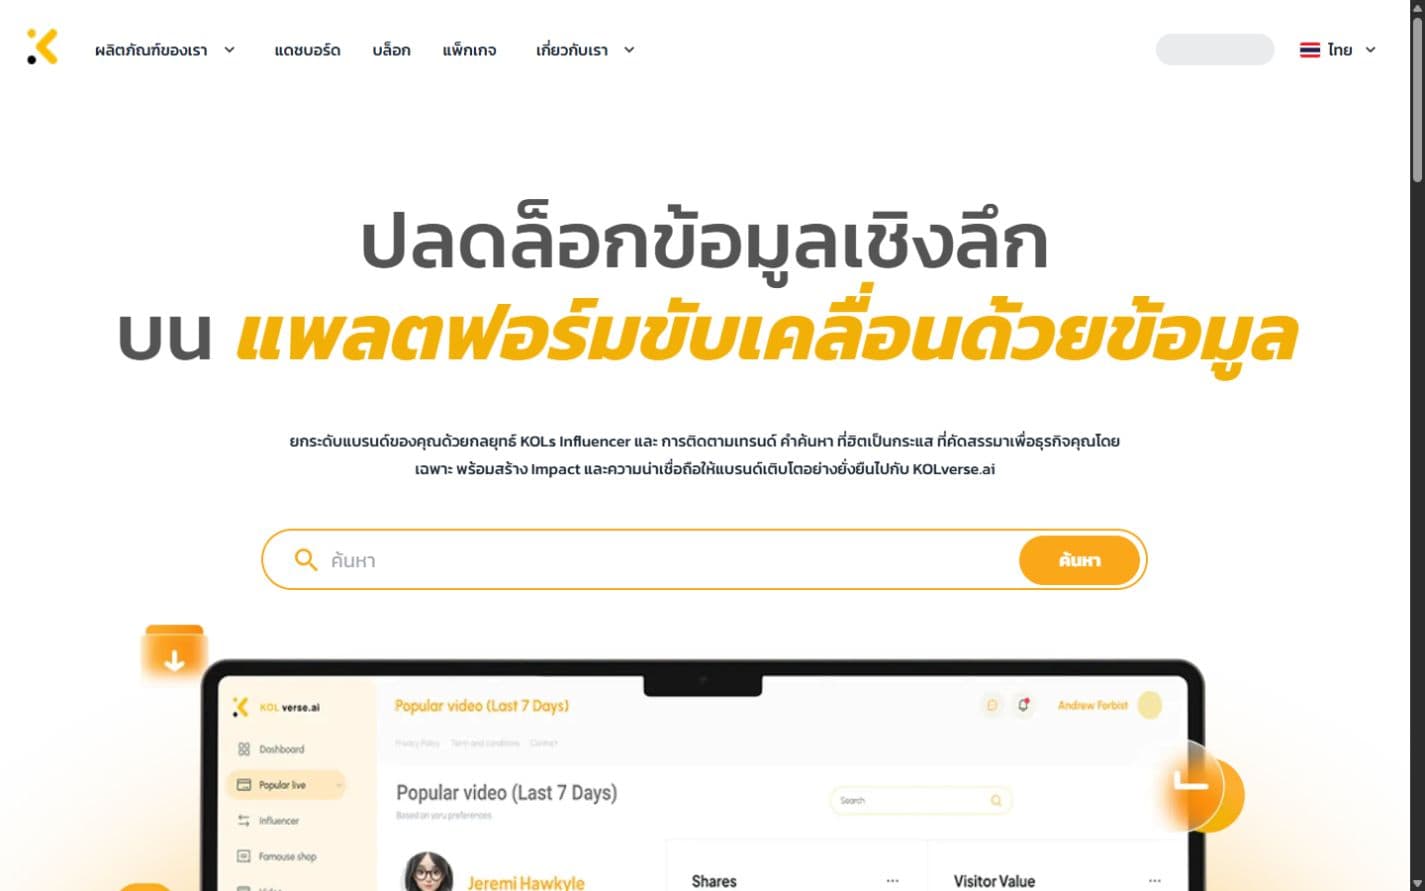
A creator-intelligence platform combining TikTok discovery, authenticated analytics, team workspaces, subscriptions, and usage controls.
TikTok creator analytics SaaS, from discovery to paid plan in one product.
- Role
- Backend lead and infrastructure owner
- Ownership
- Led the backend; owned the AWS infrastructure and Terraform
- Core stack
- Next.js · React · TypeScript · Tailwind CSS · NestJS
Brands needed to research TikTok creators, products and live sales, then pay for team access, without stitching several tools together.
What I built
- Designed the payment, subscription, affiliate, auth, plan, usage, workspace and notification modules in the NestJS API (on Bun)
- Built ChillPay checkout as a state machine: HMAC-verified webhooks processed through BullMQ, with
SELECT … FOR UPDATEon the checkout row so a retried webhook can't provision twice - Built the ingestion path from a third-party TikTok data API into Neo4j, then bulk-indexed into OpenSearch in batches of 500, with retries, exponential backoff and rate-limited fan-out
- Codified production AWS in Terraform by importing live resources into reusable modules: VPC with private subnets and NAT, ALB with host routing, ACM, Route 53, versioned and encrypted S3, least-privilege IAM
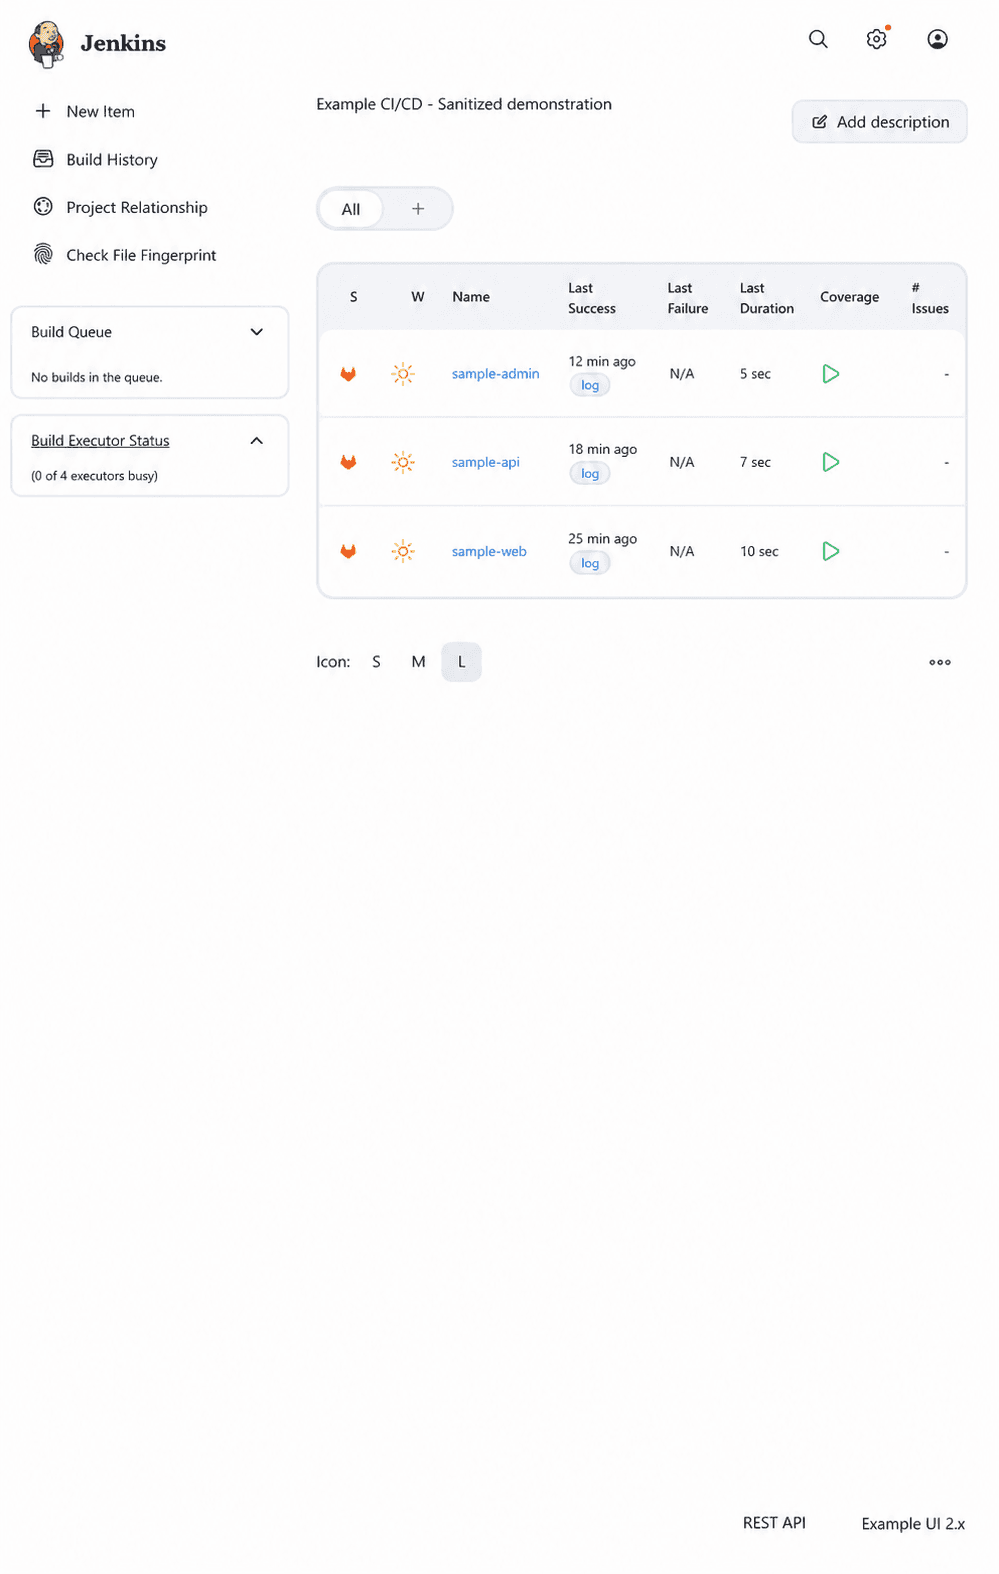
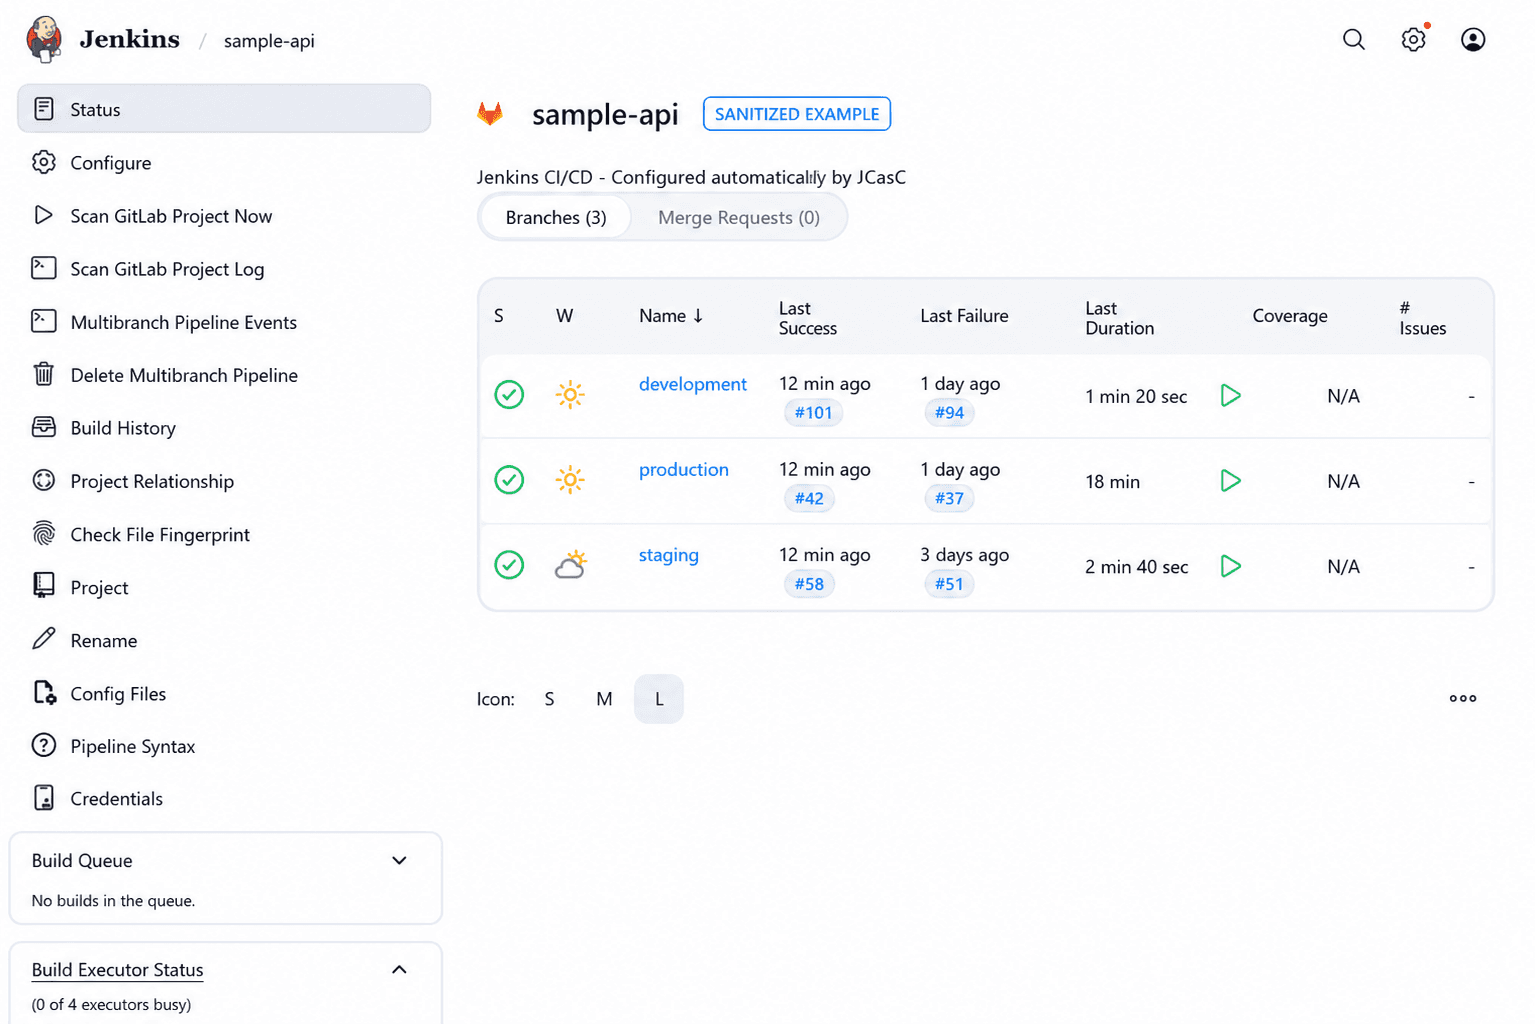
- Built three Jenkins pipelines and set up Prometheus, Loki, Grafana and Alertmanager with Telegram alerts
How it fits together
Next.js serves the public site and the authenticated product. The NestJS API owns auth, workspaces, subscriptions, payments, dashboards and search. PostgreSQL with Prisma holds transactional data, Neo4j models the creator graph, OpenSearch serves search, and Redis backs BullMQ queues and caching.
Outcome
Brands can find a creator, dig into the analytics, save the research and manage a paid team plan in one product. Payments, renewals and affiliate commissions run without manual steps.
Deep diveCore feature walkthroughAn interactive flow of the hardest workflow, step by step.
How the main product workflows operate
Payment activates access only after a verified gateway event
Checkout is treated as a state machine. The browser starts payment and can display the result, but it is not trusted to activate a subscription. ChillPay's server-to-server webhook is the authoritative transition into provisioning.
NestJS · ChillPay PayLink · BullMQ · Prisma transaction
Subscription provisioning starts from the verified webhook state, not a success query string in the browser.
The checkout row is locked and an existing subscription link is returned, preventing duplicate workspace, invoice and subscription creation.
Feature limits are copied from the purchased plan into the subscription so later plan edits do not silently rewrite an active contract.
Deep diveDelivery pipeline and AWS architectureCommit to production, Terraform foundations, and the sanitized AWS topology.
From commit to production
KOLVerse uses separate multibranch pipelines for the website, API, and admin application. Infrastructure is modeled with Terraform, while deployments produce traceable Docker images and verify service health after rollout.
GitLab branch
Multibranch discovery for development, staging, and production.
Validate
Frozen install, lint, formatting, API tests/build, and SonarQube analysis.
Build image
Date + commit SHA tags provide traceable Docker releases.
Push registry
Environment-specific images are published to GitLab Container Registry.
Deploy EC2
Jenkins updates Docker Compose remotely over credential-managed SSH.
Verify release
Host and public health checks run before Telegram notification.
Terraform-managed AWS foundations
Network boundaries
VPC, public/private subnets, internet and NAT routing.
Secure ingress
Route 53, ACM certificates, ALB listeners, host routing, and target health.
Application compute
Separate website, API, and admin workloads across production and staging.
Storage & identity
S3 assets, IAM instance profiles, encrypted volumes, and scoped permissions.
Access control
Security groups and managed SSH access protect operational entry points.
Repeatable changes
Terraform fmt, validate, reviewed plan, controlled apply, and post-apply verification.
KOLVerse AWS Architecture
The topology matches production; CIDRs, hostnames, ports, instance sizes, region and account identifiers are replaced with documentation examples. The illustrated VPC is 10.20.0.0/16 with separate Website, Admin and API target groups behind one TLS-enabled ALB.